Hospital access control: a practical deployment checklist
A hospital access-control checklist covering zones, staff, visitors, contractors, temporary rights, offline continuity, and audit.
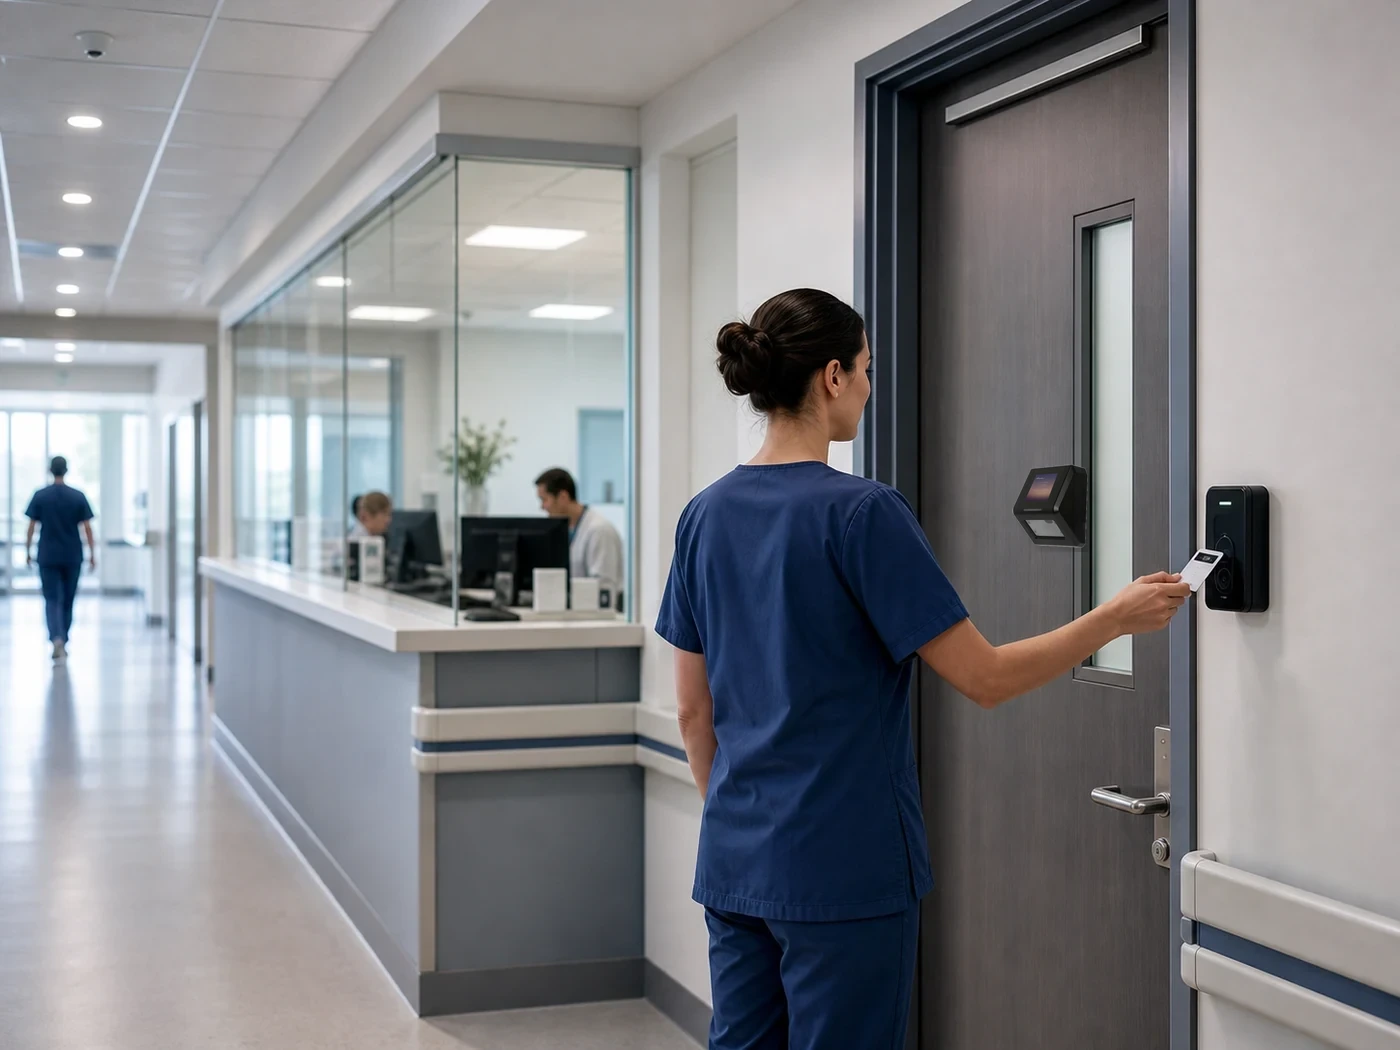
Hospitals combine high foot traffic with areas that require very different levels of control. Public lobbies, clinical departments, medicine stores, laboratories, server rooms, staff entrances, service routes, and technical areas should not share one broad access policy.
Start by mapping sites, buildings, floors, departments, zones, doors, and operational owners before choosing credentials or readers. Separate staff, rotating personnel, trainees, patients or carers where relevant, business visitors, contractors, and service teams. Permissions should be scoped by role, site, zone, schedule, purpose, start date, and expiry—not only by job title.
Visitor Management becomes useful when a visit has a host, destination, validity window, approved doors or lift floors, temporary credential, check-out or automatic expiry, and a searchable event history. Contractors should be managed by job, internal sponsor, working area, schedule, and contract end date rather than with reusable long-term cards.
Continuity must be tested in the field. Under an offline-first model, synchronized permissions are evaluated locally at the device while the server manages policy and aggregates events. Acceptance tests should cover network loss, local event storage, resynchronization, revoked rights, device time, power backup, denied attempts, and manual overrides. Life-safety and emergency-release behavior must follow the standards and technical scope applicable to each facility.
Duall Master places Access Control, Visitor Management, Attendance, Parking, Video Management, and Video Intercom on one identity, zone, policy, device, event, and audit foundation. Hospitals can begin with staff access and restricted areas, then expand by validated workflow and module.
Keep reading